Dussehra & Diwali Special
Festive Season Special Offer 2026
Flat 25% OFF on Both Diploma Courses
Celebrate Dussehra & Diwali with huge savings on career-defining tech diplomas, hands-on, expert-led training.
Our diploma courses include:
1-Year Cyber Security Diploma — Powered by AI1-Year Diploma in Artificial Intelligence & Machine Learning
Flat
25% OFF
Both Diplomas
Enroll Now
Cybersecurity vs AI: Which Career Is Better in 2027?
Let’s take a look at the differences between Cybersecurity vs AI and see which skills can help you build a bright career in the IT Industry!
P
Pawan Panwar•Oct 23, 2026
how to become a cloud security engineercloud security engineer skillscloud security engineer career path
Cloud Security Engineer Roadmap: AWS, Azure, Skills and Salary
Let’s talk about what a Cloud Security Engineer is, its knowledge, its skills, and related career benefits for IT Aspirants!
P
Pawan Panwar•Oct 22, 2026
What Is an AI SOC Analyst? Skills, Tools, and Career Opportunities
Do you know what an AI SOC Analyst is, its uses, and why several organizations are demanding professionals with such skills for better security? If not, then you are in the right place. Here, we will talk about these skills and related career benefits in detail. Moreover, we will introduce you to a reliable training institute offering a dedicated training program related to SOC analyst skills. What are we waiting for? Let’s get started! What Is an AI SOC Analyst in Cybersecurity? An AI SOC Analyst is a next-generation cybersecurity professional or autonomous software agent that leverages machine learning, natural language processing, and behavioral analytics to automate security operations. To speed up threat detection, automate warning triage, and manage crises at machine speed, they consume enormous telemetry streams from endpoints, networks, and cloud environments. AI SOC Analysts significantly shorten detection and response times by supporting traditional security teams, freeing up human analysts to concentrate on strategic defense and intricate threat hunting. Let’s explore what an AI SOC Analyst is, its knowledge, its skills, and related career opportunities in the IT Industry! How Does an AI SOC Analyst Work in a Security Operations Center? An AI SOC analyst works in a SOC in the following ways: 1. Ingests Multi-Source Telemetry: Logs from endpoints, networks, cloud, and identity platforms are continuously streamed and parsed. 2. Automates Alert Triage & Correlation: Combines relevant security events to prioritize real risks and remove harmless noise. 3. Executes Autonomous Response Playbooks: Causes immediate machine-speed containment measures, such as host isolation or credential revocation. 4. Accelerates Investigation via Copilots: Generates investigative inquiries and summarizes intricate assault chains using generative AI. 5. Performs Predictive Threat Hunting: Finds latent, persistent enemies before harm is done by analyzing baseline behavioral anomalies. AI Security Copilots and Autonomous SOC Agents S.No. Factors What? 1. AI Security Copilots Serve as real-time sidekicks that support human analysts with activities related to inquiry, triage, and response. 2. Autonomous SOC Agents Complete end-to-end security processes autonomously, without human intervention, from host containment to threat detection. 3. Human-in-the-Loop Collaboration Guarantees that important choices and significant containment measures are still subject to human approval. 4. Generative Query & Script Synthesis Converts natural language questions into automation scripts, regex patterns, and technical hunting queries. 5. Continuous Adaptive Learning Incorporates dynamic telemetry and post-event feedback to continuously improve detection logic and reduce false positives. Key Roles and Responsibilities of an AI SOC Analyst The following are some key roles and responsibilities of an AI SOC analyst: ● Automated Alert Oversight & Supervision: Keeps an eye on high-throughput AI triage feeds to guarantee precise threat classification and avoid false positives. ● Complex Escalation & Edge-Case Investigation: Examines new evasion strategies that go around autonomous detection filters and multi-stage zero-day attacks. ● Agent Governance & Skill Tuning: Enhances automation playbooks, detection logic, and AI prompts to maximize agent accuracy and stop model drift. ● Proactive & Hypothesis-Driven Threat Hunting: Searches enterprise telemetry for subtle signs of compromise and latent dangers using AI copilot queries. ● Strategic Stakeholder & Compliance Communication: Creates concise executive briefings, incident reports, and regulatory documentation based on technical AI threat assessments. Real-Time Incident Triage, Automated Playbook Execution, and Threat Hunting In order to prioritize high-confidence risks as they appear throughout the organization, real-time incident triage rapidly filters noise and correlates multi-source data. AI SOC Analysts instantly contain machine-speed attacks while continuously looking for persistent, hidden zero-day adversaries by combining automated playbook execution with proactive threat hunting. Essential Technical and Soft Skills Required for an AI SOC Analyst S.No. Factors What? 1. Prompt Engineering & Natural Language Querying Creates accurate natural language queries to extract security copilots' danger context. 2. Behavioral Telemetry & Anomaly Analysis Identifies unusual activity by interpreting complicated logs from endpoints, networks, and identities. 3. AI Model Tuning & Playbook Governance Improves automation playbooks, prompt templates, and detection rules to stop model drift. 4. Critical Thinking & Adversarial Intuition Verifies AI outputs to identify subtle strategies used by attackers to evade automated logic. 5. Crisis Communication & Strategic Reporting Converts intricate descriptions of AI incidents into executive briefings that are clear and useful. Top AI-Powered SOC Tools and Technologies The following are the top AI-powered SOC tools and technologies: a) AI-Driven Next-Gen SIEM & Data Lakes: Centralizes high-throughput company logs for economical analytics and real-time machine learning detection. b) Autonomous Extended Detection & Response (XDR): Blocks multi-stage threats in real time by correlating endpoint, network, identity, and cloud telemetry. c) AI Security Copilots & Conversational Assistants: Automatically generate hunting queries, summarize occurrences, and expedite triage by ingesting simple-language instructions. d) Autonomous SOC Agents & AI Triage Bots: To quickly pinpoint affected assets, validate risks, and filter out noise, evaluate raw security alerts independently. e) Agentic SOAR & Hyper-Automation Engines: Automate end-to-end incident containment and remediation by initiating dynamic, multi-system orchestration workflows. AI-Driven XDR, SIEM, and SOAR Platforms The following are some factors related to AI-driven XDR, SIEM, and SOAR platforms: 1. AI-Driven Next-Gen SIEM: Identifies complex, cross-domain threats in real time by ingesting and correlating high-throughput corporate logs. 2. Autonomous Extended Detection & Response (XDR): Combines identity, network, cloud, and endpoint telemetry to instantly stop multi-stage assaults. 3. Agentic Security Orchestration, Automation, and Response (SOAR): Creates and implements adaptive response procedures across various security systems in a dynamic manner. 4. Unified Decision & Reasoning Layer: Creates high-confidence attack verdicts by synthesizing context from many security tools. 5. Adaptive Continuous Learning Loop: Automatically improves detection logic by continuously incorporating new telemetry and post-incident input. AI SOC Analyst vs Traditional SOC Analyst: Key Differences S.No. Topics Factors What? 1. AI SOC Analyst Workload & Focus Use copilots and automated agents to manage high-throughput triage, concentrating human labor only on difficult investigations, edge cases, and strategic danger hunting. Skill Set Requires knowledge of behavioral analytics, rapid engineering, machine learning model governance, and directing autonomous workflow execution. 2. Traditional SOC Analyst Workload & Focus Carries out repetitive log correlation across several security products, validates false positives, and manually prioritizes high-volume warnings most of the time. Skill Set Uses strict step-by-step SOC runbooks, rule-based detection logic, manual IP/hash lookups, and static SIEM query languages. How to Become an AI SOC Analyst: Step-by-Step Career Roadmap? You can become an AI SOC analyst in the following ways: ● Master Core Security & Telemetry Fundamentals: Develop a solid foundation in MITER ATT&CK, event log structures, operating system internals, and TCP/IP. ● Develop AI, ML, & Data Literacy: Discover MITER ATLAS framework approaches, LLM mechanics, prompt crafting, and output evaluation. ● Gain Hands-On Experience with Modern Security Stacks: Learn how to set up, query, and administer AI-powered SOAR, SIEM, and XDR systems. ● Earn Target AI & Cyber Security Certifications: Acquire foundational credentials such as Security+, BTL1, or specific AI security certifications. ● Build an Applied Portfolio & Practice Human Governance: Post lab case studies, agent supervision logs, and custom detection-as-code rules to GitHub. Best Certifications and Training Courses for AI SOC Analysts The following are some of the best certifications and training courses for AI SOC analysts: a) Nvidia Certified Associate / Custom AI Sec Badges: Verifies fundamental expertise in hardware acceleration, AI process integration, and deployment approaches. b) ISC2 AI Security Certificate / GIAC GAIPS: Certifies proficiency in generative AI and LLM deployment pipeline auditing, security, and governance. c) Microsoft Certified: Security Operations Analyst Associate (SC-200): Demonstrates proficiency with Defender XDR, Security Copilot, and Sentinel environments. d) Blue Team Level 1 (BTL1) / CompTIA CySA+: Lays the fundamental practical groundwork for incident response, log analysis, and operational triage. e) Stanford Online AI Security / EICTA IIT Kanpur GenAI in Cybersecurity: Offers a scholarly foundation in automated detection, rapid engineering, and AI threat modeling. AI SOC Analyst Salary in India and Global Career Opportunities S.No. Job Profiles Salaries 1. AI Security Operations Analyst ₹30,000 - ₹2,50,000+/ month 2. Detection & Automation Engineer ₹32,000 - ₹3,50,000+/ month 3. AI Security Prompt & Skill Manager ₹40,000 - ₹4,58,000+/ month 4. Cyber Threat Intelligence (CTI) AI Specialist ₹37,500 - ₹5,08,000/ month 5. AI Security Governance & Risk Manager ₹1,25,000 - ₹5,00,000+/ month Future Scope of AI SOC Analysts and the Impact of AI on Cybersecurity Jobs In the future, proactive threat design, fast engineering, and high-level system governance will replace human log inspection in SOC operations. AI transforms human analysts into strategic orchestrators who oversee autonomous defensive ecosystems and control machine-speed risk, rather than displacing them. Conclusion Now that we have talked about what an AI SOC Analyst is, you might want to learn more about such skills professionally from a reliable source. For that, you can go for the Certified Security Operations Center (SOC) Analyst Training Program offered by Craw Security. During the training sessions, students will be able to test their knowledge on various tasks using the SOC skills under the supervision of SOC professionals. Moreover, online sessions will facilitate remote learning for students. After the completion of the Certified Security Operations Center (SOC) Analyst Training Program offered by Craw Security, students will receive a dedicated certificate validating their honed knowledge & skills during the sessions. What are you waiting for? Contact, Now! Frequently Asked Questions About AI SOC Analyst 1. What is an AI SOC analyst? An AI SOC Analyst is a sophisticated cybersecurity position or autonomous system that employs automated playbooks, machine learning, and natural language processing to quickly identify, prioritize, and contain threats. 2. Is a SOC analyst high-paying? Yes, a SOC analyst position offers above-average income; it starts decently at entry level (65k–95k USD/₹3.5–6 LPA in India) and swiftly scales to high-paying tiers (120k–180k+ USD/₹15–25+ LPA) as analysts specialize in advanced threat hunting, incident response, and AI-driven automation. 3. Will AI replace SOC analysts? No, AI won't take the job of human SOC analysts; rather, it will automate repetitive Tier-1 alert triage, freeing up analysts for higher-value strategic positions like threat hunting, detection engineering, and AI model governance. 4. Is a SOC analyst a hard job? Although AI techniques are greatly minimizing repetitive fatigue, it is still a difficult profession because of the high alert volume, night shifts, and the stress of preventing big breaches. 5. Is a SOC analyst an IT job? Yes, a SOC analyst is a specialist cybersecurity position inside the larger IT industry that focuses more on data, networks, and systems protection than on infrastructure management or general IT assistance. 6. Is cybersecurity a dying field? No, cybersecurity is growing quickly, with millions of open positions worldwide and skyrocketing demand brought on by cloud adoption and threat landscapes of the AI era. 7. Why did SOAR and outsourced triage stop being enough? SOAR and outsourced triage have stopped being enough for the following reasons: a) Static Playbook Limits, b) Extreme Maintenance Overhead, c) Context-Blind Outsourced Triage, d) Machine-Speed Attack Timelines, and e) Ineffective Triage vs. Deep Investigation. 8. What is the difference between an AI SOC analyst and an AI threat hunter? An AI Threat Hunter proactively employs AI models to look for hidden, undetected enemies already lurking within the network, whereas an AI SOC Analyst concentrates on reacting to, triaging, and responding to incoming warnings surfaced by AI technologies. 9. How do you tell a real investigation from enrichment? A true investigation connects that context across time and telemetry to establish intent, validate an attack chain, and reach a conclusive decision, while enrichment only gathers context around an alarm, such as examining an IP's reputation or user details. 10. How do you verify the accuracy of an AI SOC analyst? You can verify the accuracy of an AI SOC analyst in the following ways: a) Red Teaming & Adversarial Simulation, b) Human-in-the-Loop Validation, c) Precision & Recall Benchmarking, d) Ground-Truth Backtesting, and e) Model Drift & Hallucination Auditing. 11. What does an AI SOC analyst not solve? An AI SOC analyst cannot replace human accountability for crucial incident response decisions, repair malfunctioning upstream telemetry pipelines, or independently provide missing organizational business context.
P
Pawan Panwar•Oct 21, 2026
Non-Verbal Communication: The Key to Confidence and Professional Success
Understand the significance of non-verbal communication, including body language, facial expressions, eye contact, and gestures, to enhance confidence and boost career success.
P
Pawan Panwar•Oct 19, 2026
Online vs Classroom AI and Machine Learning Course: Which Is Better?
Let’s take a look at Online vs Classroom AI and Machine Learning Course and explore which one is more feasible for you!
P
Pawan Panwar•Oct 9, 2026
Top 10 AI Tools Every Student Should Use in 2026
Let’s take a look at the 10 AI Tools Every Student Should Use, their uses, their features, and related benefits for the users!
P
Pawan Panwar•Oct 8, 2026
Interpersonal Communication and Its Importance
Learn the importance of interpersonal communication, its key skills, benefits, and role in career development, teamwork, relationships, and professional success.
P
Pawan Panwar•Oct 7, 2026
Communication Skills and Their Importance in Career Growth
Learn the importance of communication skills for students and professionals. Discover how effective speaking, listening, and interpersonal skills improve confidence, teamwork, and career success.
P
Pawan Panwar•Oct 5, 2026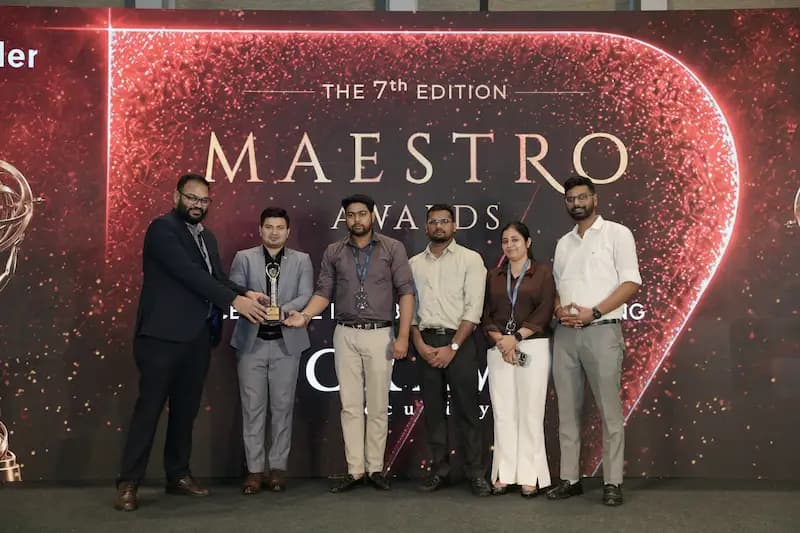
Craw Security Sponsored BSides Ahmedabad 2026 for Cyber Awareness Campaign
Craw Security sponsored BSides Ahmedabad 2026, promoting cybersecurity awareness, showcasing PhishNext, ShieldXDR, ThreatFusionAI, OSINT, and CrackTheLab, and connecting with cybersecurity and defence leaders.
P
Pawan Panwar•Oct 4, 2026
CEH and Penetration Testing: Learn Ethical Hacking & VAPT
Let’s find out the difference between CEH and Penetration Testing and see how you can learn such skills for better security!
P
Pawan Panwar•Oct 1, 2026
Active Listening Skills: Importance, Benefits, and Role in Personality Development
Learn the importance of active listening skills in personality development, communication, workplace success, and career growth. Discover techniques to improve listening abilities for professional and personal success.
P
Pawan Panwar•Sep 30, 2026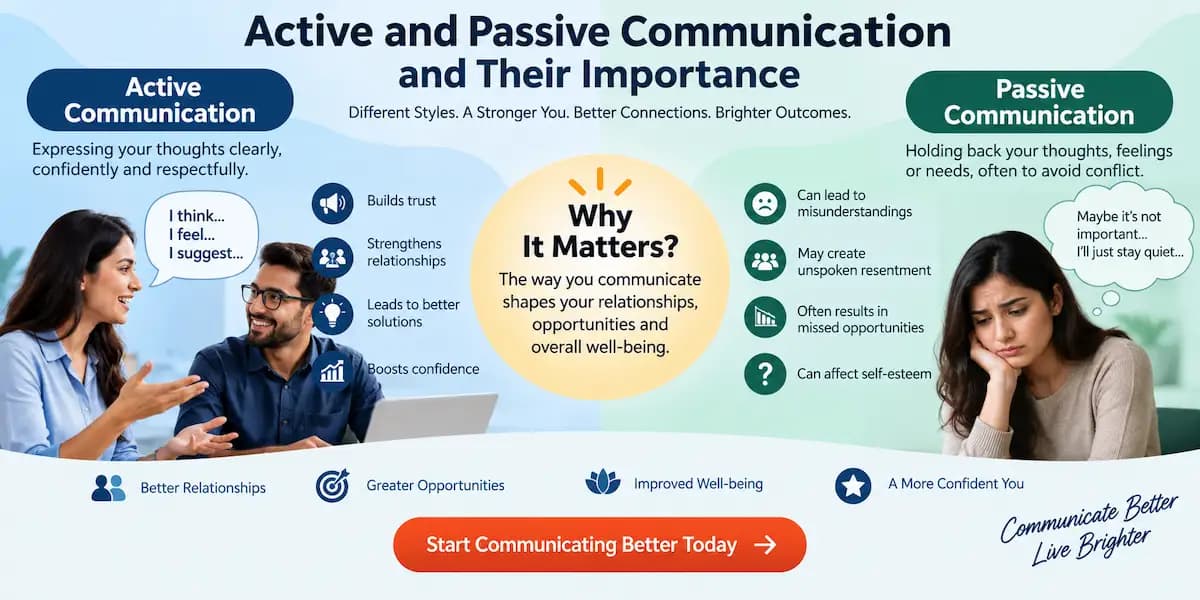
Active and Passive Communication and Their Importance
Learn the difference between active and passive communication, their importance, benefits, challenges, and how developing active communication skills can improve confidence, relationships, teamwork, and professional success.
P
Pawan Panwar•Sep 21, 2026
Top 10 SIEM Tools For 2026: Splunk, Sentinel, QRadar & More
Let’s take a look at what SIEM Tools are, their uses, their features, and related benefits for organizations in the IT Industry!
P
Pawan Panwar•Sep 20, 2026
What is Secure Shell (SSH) and How Does It Work?
Learn what SSH is, how Secure Shell works, SSH port 22, authentication, SSH keys, tunneling, security risks, uses, and best practices with Craw Security.
P
Pawan Panwar•Sep 17, 2026
The “Busy but Lost” Problem: When Students Work Hard but Have No Direction
Find more details regarding the “Busy but Lost” Problem, When Students Work Hard but Have No Direction, through this blog post by Craw Security.
P
Pawan Panwar•Sep 15, 2026